Private document storage
Original PDFs, signatures, completed PDFs, audit certificates, and organization logos are stored as private objects. Clients receive controlled, short-lived access when authorization or secure-token checks succeed.
Security and evidence
PuntSign treats document privacy, recipient access, authorization, hashes, and audit evidence as parts of the agreement workflow rather than separate add-ons.
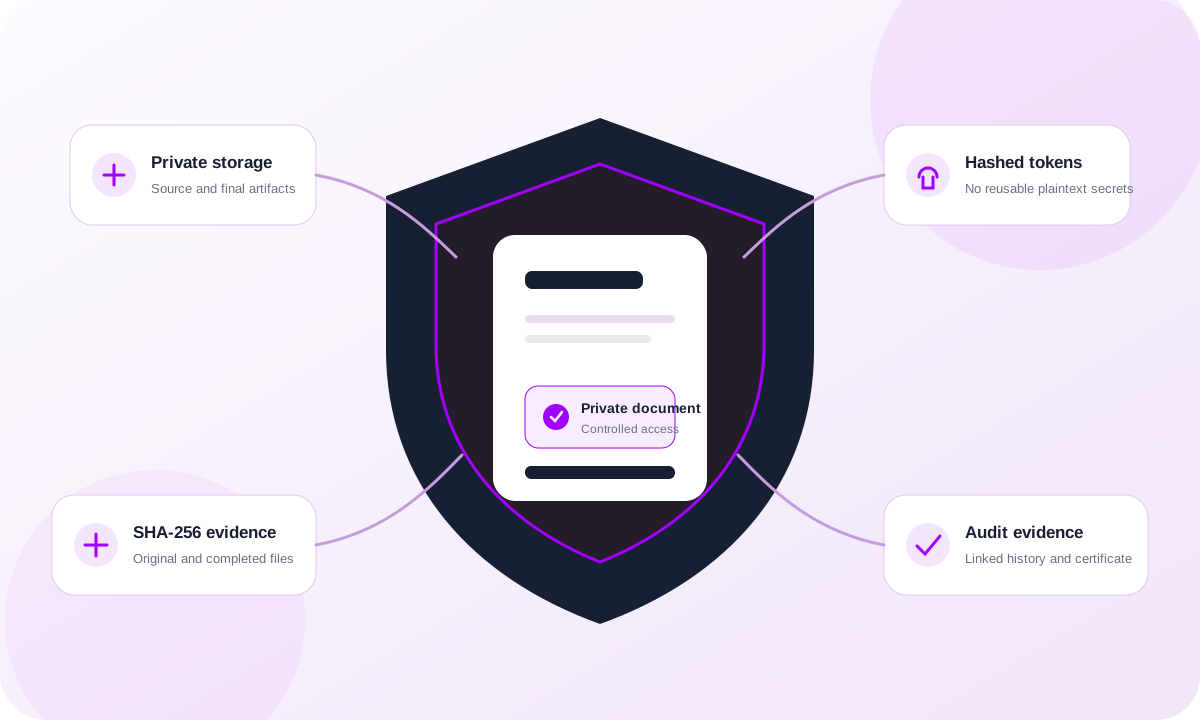
Original PDFs, signatures, completed PDFs, audit certificates, and organization logos are stored as private objects. Clients receive controlled, short-lived access when authorization or secure-token checks succeed.
Invitation, signing, session, and download tokens are stored as hashes rather than as reusable plaintext credentials in application data.
Recipients exchange email access for a bounded signing session instead of keeping an unrestricted signing link active indefinitely.
Organization membership and roles determine who can manage agreements, documents, team access, templates, branding, and administrative settings.
SHA-256 values are recorded for the source PDF and the finalized PDF so the evidence set can identify the exact document bytes associated with the workflow.
Material actions are recorded in a cryptographically linked audit history, and the completed workflow produces a separate audit certificate alongside the final PDF.
Document evidence
The completion workflow does not overwrite the source PDF. It creates a separate finalized document from the original plus submitted values, records the completed hash, and produces a separate audit certificate.
Scope matters
PuntSign provides application security controls and electronic agreement evidence, but the current MVP does not claim capabilities that require separate trust services, regulated identity infrastructure, or notarization networks.
Certificate-based digital signatures, qualified electronic signatures, remote notarization, government identity verification, AI contract review, and contract negotiation are not part of the current product scope.
Review how recipient access, routing, finalization, private storage, document hashes, and audit evidence connect across the full agreement lifecycle.